Field notes from an AI-native security practice
How real startup apps break, how AI surfaces get attacked, and what to fix first.
More posts
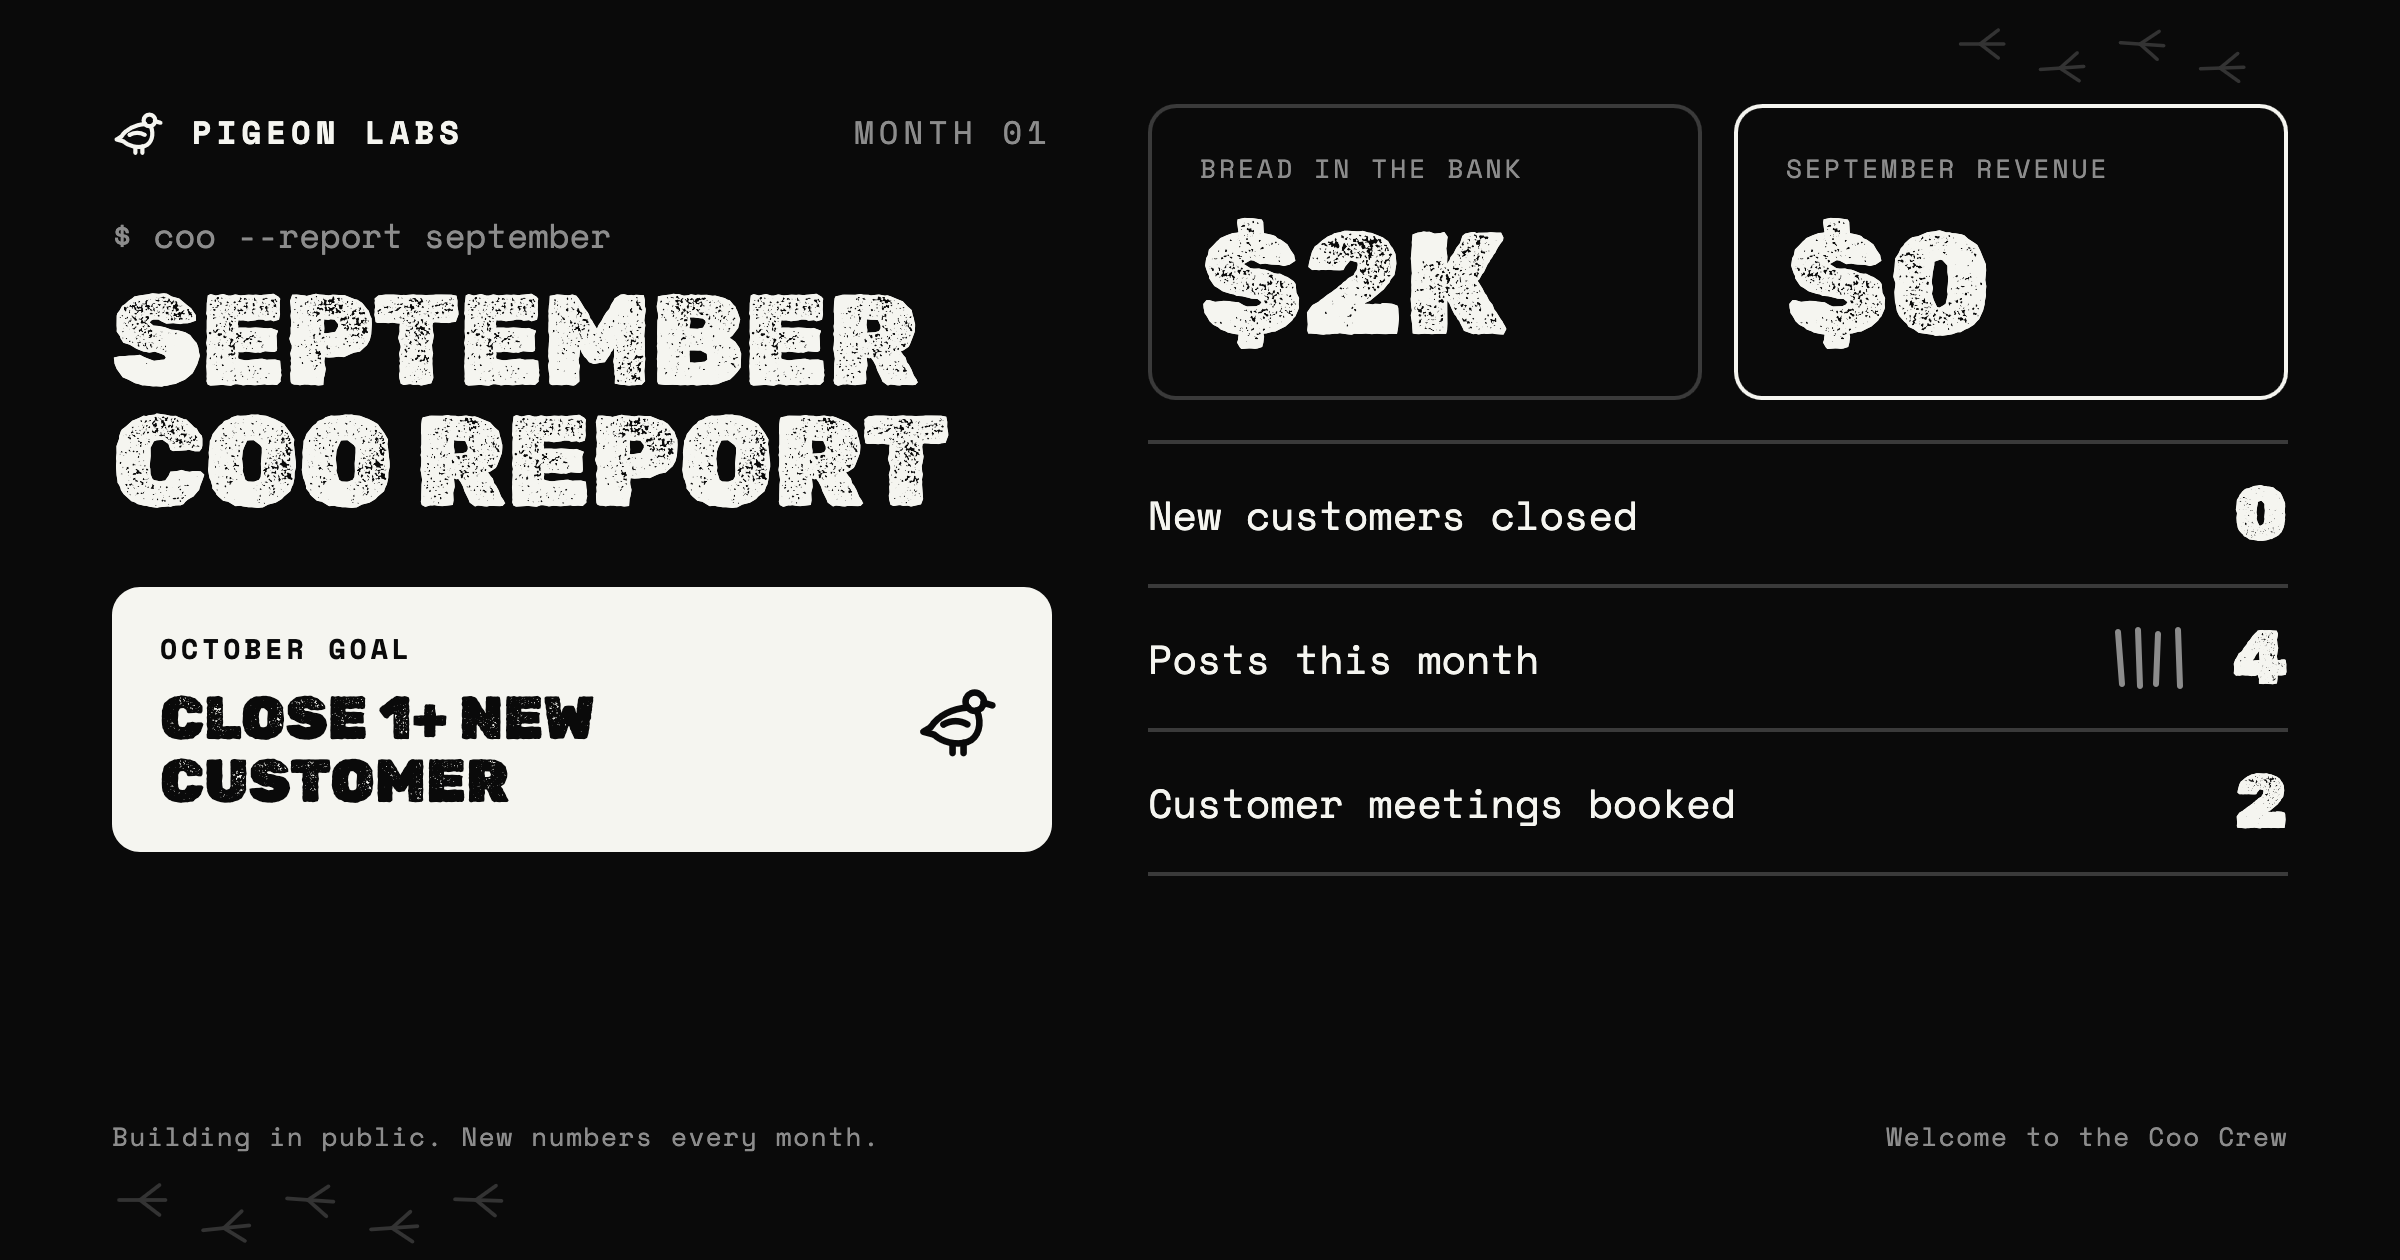
$2k in the Bank and Zero Revenue
Pigeon Labs September Investor Update
Pigeon Labs
Breaking Down Appsec Part 6: Let's build a model!
Threat Modeling is often done poorly due to a lack of understanding
Pigeon Labs
Breaking Down Appsec Part 5: You Have no Business Here (Business Logic Flaws)
Appsec is about where everything could go wrong, not just about the latest hacks
Pigeon Labs
Breaking Down Appsec Part 4: Following the Trail (Taint analysis)
Part of appsec and hacking is about understanding how to connect the dots
Pigeon Labs
Breaking Down Appsec Part 3: Securing the Perimeter (Authority/Authorization)
The first steps to secure your application after you know your application is to secure from the outside in
Pigeon Labs
Breaking Down Appsec Part 2: Securing the Perimeter (Identity)
The first steps to secure your application after you know your application is to secure from the outside in
Pigeon Labs
Breaking Down Appsec Part 1: Application Context
Appsec starts from knowing everything
Pigeon Labs
What really is application security (appsec)?
What appsec covers, and why it isn't a compliance checklist
Pigeon Labs
What are we doing?
Doing cyber things like an adult - on our own :') but with the support of our friends who believe in us
Pigeon Labs
I gave my AI agent hands
Give Hermes agent a way to have frictionless deployment with Vals
Pigeon Labs
How to Hack Every AI Agent Ever
The secret sauce to exploiting agents
Pigeon Labs
Three Security Mistakes Almost Every AI Agent Startup Is Making Right Now
I hack AI agents for a living.
Pigeon Labs
I Hack AI Agent Startups With a Bug From 2011
The Vulnerability in Almost Every AI Agent Nobody's Patching
Pigeon Labs
Right Guardrail, Right Place?
Part 4 of the D2 Blog Series: “Authorization in the Age of Agents”
Pigeon Labs
From Guardrails to GuardFails
Part 3 of the D2 Blog Series — “Authorization in the Age of Agents”
Pigeon Labs- From Words to Actions: Why LLMs Need Real Security
From Words to Actions: Why LLMs Need Real Security
Part 2 of the D2 Blog Series — “Authorization in the Age of Agents”
Pigeon Labs - Why Agentic Systems Are Dangerous by Design
Why Agentic Systems Are Dangerous by Design
Part 1 of the D2 Blog Series — “Authorization in the Age of Agents”
Pigeon Labs
Don't miss the next one.
New research on AI agent security, delivered when it matters.