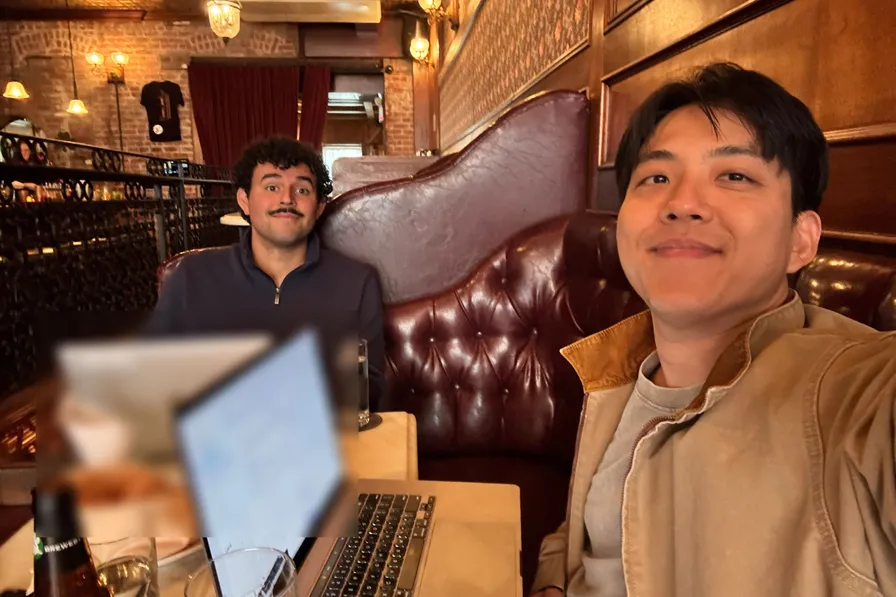
About Pigeon Labs
We're ex-Amazon engineers who help startups pass security reviews and close their enterprise deals.
- Ex-Amazon pentesters and AppSec engineers
- 5 days of testing, report the next day
- NYC area, onsite when you need us
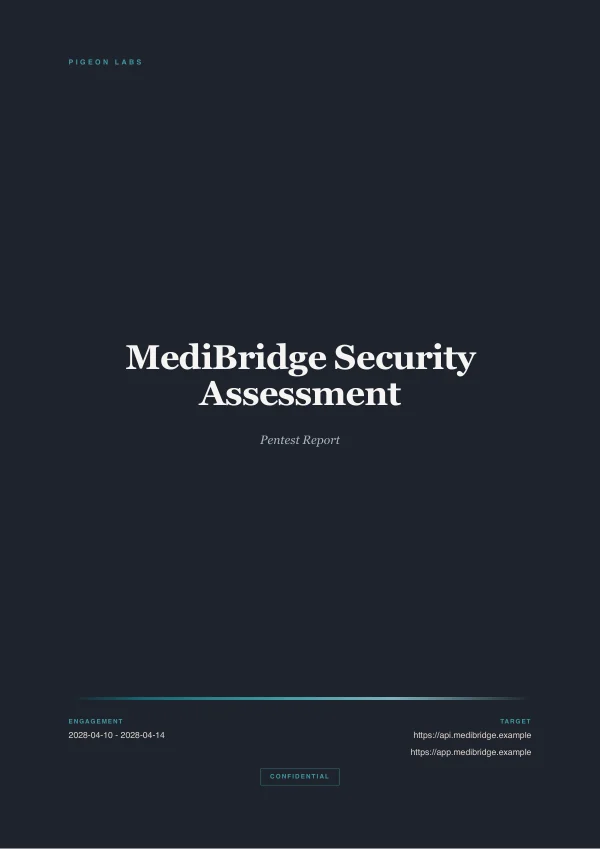 View a sample report
Why we started
We kept hearing the same story from founders. A big customer is ready to sign, then their security team sends a questionnaire asking for a recent pentest, and the deal stalls or dies. Some of those founders lost hundreds of thousands in ARR that way. We started Pigeon Labs so fewer founders have to go through that.
David Kim & Daniel Chalco, co-founders
Why founders call us
A buyer asked for a pentest.
Enterprise security teams usually want a recent third-party report before they sign. You get one written for them, with findings ranked by what to fix first.
An audit is coming up.
SOC 2, ISO 27001 and HITRUST auditors usually expect evidence of security testing. Our report is written so you can hand it straight to your auditor.
You handle health data.
HHS has proposed making a yearly pentest part of the HIPAA Security Rule. Testing now means you're ready if it becomes final.
Your insurer is asking.
Cyber insurance applications often ask about recent security testing. A report gives you a straight answer.
You ship AI agents.
We try to trick your agents into misusing their tools or handing one customer's data to another, before someone else does.
What you get
A pentest of your app and APIs
We break in the way a real attacker would, then rank what we find by what to fix first.
AI agent testing
For agents that can read customer data or take actions.
A plain-English report
One you can send to a buyer's security team or your auditor. See a sample report
Fixes, if you want them
We can write the fixes too, so your engineers keep shipping.
When a deal is waiting
Ask about our rush option. We're based in the NYC area and happy to come onsite.